A multi-tenant architecture lets one software platform serve many customer organizations, called tenants, while keeping each tenant's data, configuration and users separate. For general business tools that separation is a matter of privacy. For financial software it is a matter of control: a ledger, a payroll run or a list of counterparties that leaks into another tenant, or that the wrong employee can change, is an accounting and legal problem, not just a technical one
This guide explains the main data isolation options in plain terms, then covers what really decides whether a financial system is safe to share: role-based access control, contracted entitlements, least privilege, separation of duties, owned service accounts, access reviews, same-day offboarding, audit logs and the customer's right to its own data, keys and backups
What multi-tenancy means for financial systems
In a single-tenant setup every customer runs its own copy of the application and its own infrastructure. In a multi-tenant setup customers share some layers, such as the application code or the hosting platform, and the software enforces the boundary between them. Most modern platforms sit somewhere between the two extremes, and the right point depends on risk, regulation, cost and how much customization each customer needs
For a finance team, a tenant is rarely one company. It is usually a group: several legal entities, several currencies, shared service teams and outside parties such as an accountant or auditor who need limited views. A sound design therefore isolates tenants from each other and also controls access inside the tenant, down to the entity, module and action
Why finance raises the bar
- Ledger entries, bank balances and payroll data are confidential and often regulated
- A wrong change to a posted figure affects reports, taxes and decisions downstream
- Auditors need to see who did what, when and with what approval
- Integrations with banks, gateways and providers create machine access that must be governed like human access
Data isolation approaches explained
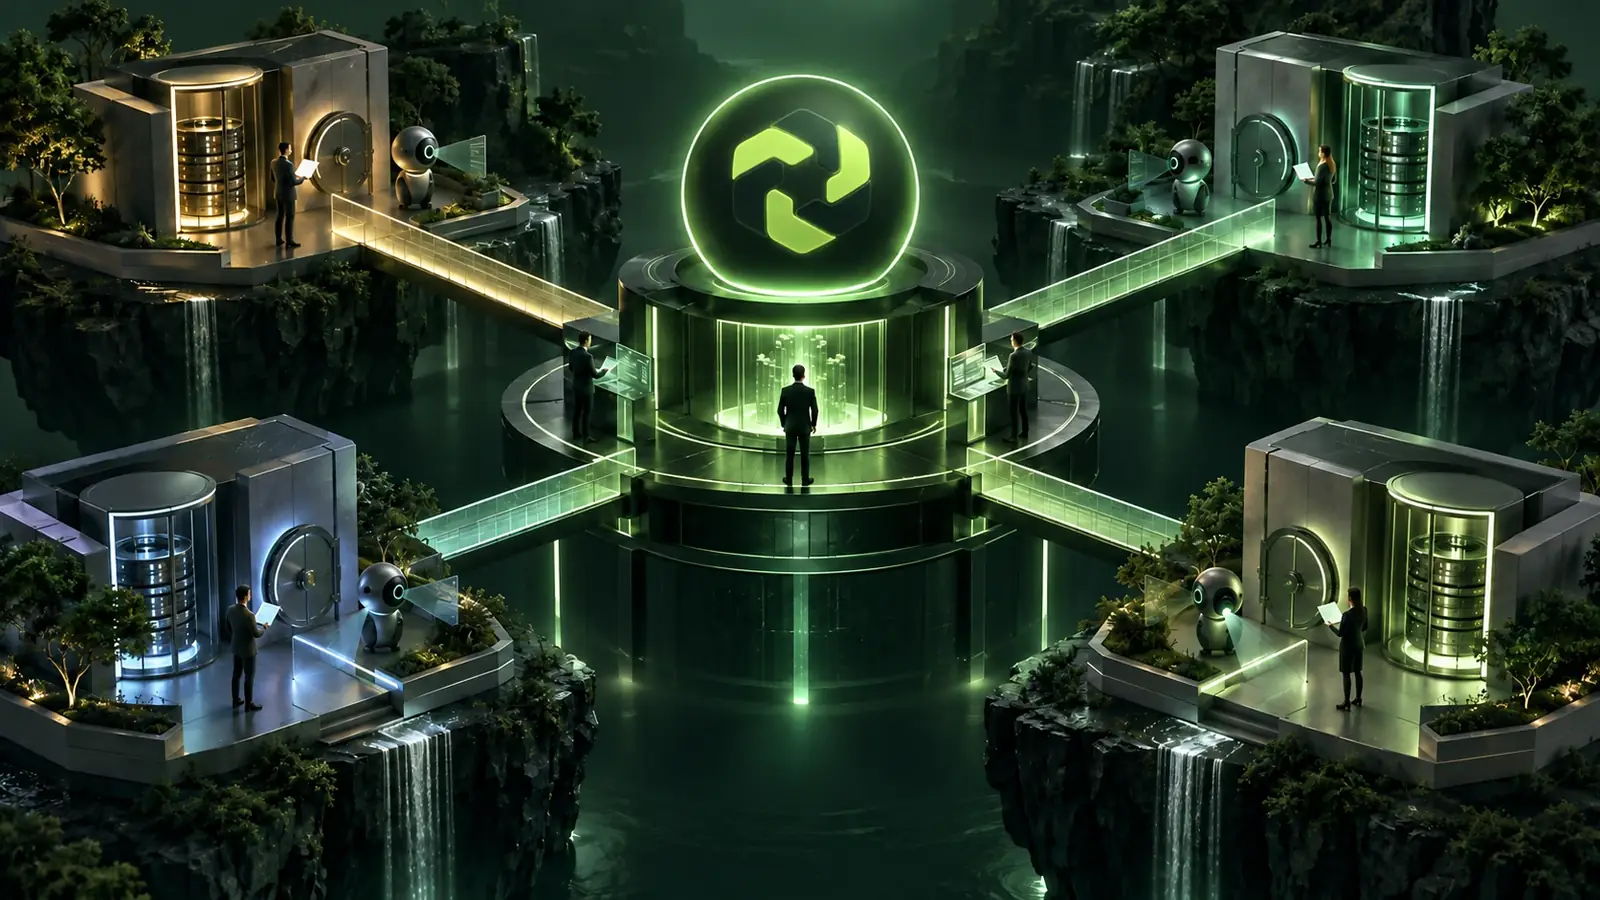
Data isolation is the set of measures that stop one tenant's records from being read or changed by another. There is no single correct pattern; each option trades cost and operational simplicity against the strength and visibility of the boundary
Shared database with a tenant identifier
All tenants live in the same tables, and every record carries a tenant identifier that the application filters on. This is efficient and easy to upgrade, but the boundary depends entirely on the application applying that filter correctly on every query, report and export, so testing and code review carry most of the weight
Separate schema or separate database per tenant
Each tenant gets its own set of tables or its own database while possibly sharing servers. The boundary becomes easier to see and to back up or restore per customer, at the price of more operational work when the number of tenants grows
Separate infrastructure per tenant
The tenant runs on dedicated servers or a dedicated environment. This gives the clearest separation and the most freedom over location and change windows, and it costs the most to operate. Groups with strict internal policies or regulators' expectations often prefer it
At Arfinex, customer data and access are always separated, and the level of infrastructure, database and backup isolation is specified and verified in each deployment plan rather than promised in general terms. That plan states where data lives, how backups are separated and how isolation is tested before go-live, so the answer matches the customer's risk instead of a sales slogan
Role-based access control, entitlements and least privilege
Isolation between tenants is only half of the picture. Inside a tenant, role-based access control decides what each person can see and do. Permissions are attached to roles such as payables clerk, treasury officer, controller or external auditor, and people receive roles instead of individually crafted rights. This makes access explainable: you can show an auditor a role matrix rather than hundreds of personal exceptions
Entitlements sit one level above roles. They describe what the customer has contracted, and therefore which modules are enabled for the tenant at all. If a group has contracted ledger, close and reporting but not payroll, the payroll module stays switched off for every user, whatever their role. Keeping entitlements separate from roles prevents a generous role from quietly opening functionality the organization never agreed to use
Least privilege is the rule that ties both together: every person, agent and integration gets the minimum access needed for its task, for the entities it serves, and only for as long as it needs it. In practice that means a few clear defaults
- Read-only by default, with write and approve rights added deliberately
- Access scoped to the legal entities and modules a person actually works on
- Administrative rights held by named people, never by a shared account
- Two-step sign-in for sensitive roles, as defined in the security plan
- Specialist AI agents with explicit authority boundaries: a reconciliation agent can propose matches, but cannot post or approve them
Separation of duties and approvals
Separation of duties means that no single person can both create and finalize a sensitive financial action. In Arfinex, adjustments, opening balances, post-hoc rate changes, reopening closed periods and transfers above limits need two separate people: one records, one approves. The system enforces this, so the control does not depend on someone remembering a policy document
This works because the ledger is the reference system. Every balance change is an event with a balanced double entry, and mistakes are corrected with reversing entries rather than by editing or deleting. Our article on the immutable double-entry ledger and its audit trail explains why that design makes access control verifiable after the fact
AI follows the same discipline. Totals, rates, fees, postings and period close run on deterministic, testable code; AI proposes and explains, and its output is labelled as a proposal until a person with the right role accepts it
Service accounts, integrations and audit logs
Much of the access in a financial platform belongs to machines: bank feeds, payment gateways, reporting exports and automation flows. A service account without an owner is an open door that nobody reviews. Every service account and API key should therefore have a named owner, a stated purpose, a minimal scope and a review date
Arfinex connects external tools through governed flows in which each flow has an owner, an execution log, failure alerts and a stop switch, and keys are entered into a vault by the customer rather than shared in conversations. The integration hub and end-to-end automation service describes how those flows are built and monitored
Audit logs close the loop. A useful log records who acted, on which tenant and entity, what changed, when, from which session and under which approval. Logs must be protected from editing by the people whose activity they record, and auditors should get read-only access to them instead of exports prepared by the team under review
Access reviews and same-day offboarding
Access drifts. People change teams, projects end and temporary rights become permanent. A simple lifecycle keeps the role matrix honest
- Joiner: the manager requests a role, and a second person approves it before access is granted
- Mover: when someone changes position, the old role is removed at the same time the new one is added
- Leaver: access, sessions, keys and delegated approvals are revoked on the same day the person leaves
- Periodic review: owners confirm every user, role, service account and API key, and anything unconfirmed is removed
- Evidence: each review is stored with the reviewer's name and date so an auditor can trace it
Arfinex's technical governance, security and access service covers these reviews, activity logging, secrets in a vault and backups that count only after a restore test. Where a tenant also needs to know its customers and counterparties, identity verification, KYB and compliance runs through licensed providers and records every decision with evidence
Ownership of data, keys and backups
A secure shared platform must still leave the customer in charge. In Arfinex the customer owns its data, configuration, keys and backups, a full export is possible at any time, and suspending the service never deletes or holds data hostage. That ownership is part of security: an organization that cannot leave cannot fully control its own risk
Ownership also shapes delivery. Design and build happen in a sandbox with synthetic or anonymized data, a parallel run compares the new system with the current method, and go-live happens only with the customer's approval. Live financial data does not need to touch the build environment to prove that isolation and roles work
Checklist for evaluating a multi-tenant financial platform
Whatever vendor you assess, ask for specific answers and evidence instead of general assurances. The questions below fit a first security conversation
- Which isolation model applies to our infrastructure, database and backups, and how is it verified before go-live?
- How are entitlements separated from roles, and who can enable a new module?
- Can you show the role matrix and the approval rules for sensitive actions?
- Does every service account and API key have a named owner and a review date?
- How quickly is access removed when someone leaves, and how is that evidenced?
- What do audit logs record, and can auditors read them without help from the team under review?
- How do we export all our data, and who holds the keys and backups?
A platform that answers these clearly, as part of a wider financial operating system, gives finance leaders a multi-tenant architecture they can defend in front of a board or an auditor
Isolation is the start, governed access is the proof
Choosing a data isolation model matters, but the controls a finance team relies on every day are roles, entitlements, least privilege, separation of duties, owned service accounts, reviews and logs. When those are enforced by the system and the customer keeps ownership of its data and keys, a shared platform can meet the expectations of controllers and auditors